
The 24-Hour vs. 5-Day Divide: Why CEOs and CISOs Can't Agree on Recovery Times
- By Lachlan Colquhoun
- July 20, 2025
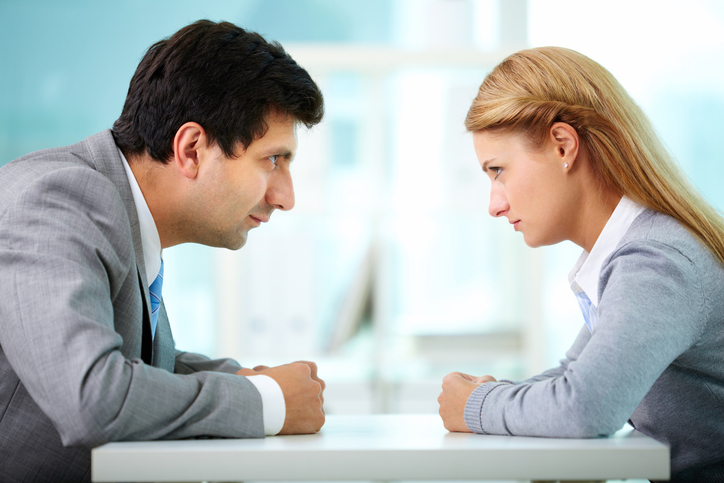
Expectations on recovery from cyberattacks, says Martin Creighan, all depend on who you speak with.
Suppose the person is the chief information security officer or someone at the forefront of the technology business. In that case, you receive a significantly different response than if you speak with someone who has a seat at the boardroom table, such as the chief executive officer or the chief financial officer.
The disparity is laid out in the fifth edition of ‘The State of Data Readiness,’ a research project by security firm Commvault. Where 80% of businesses expect to recover from a cybersecurity incident within five days, 23% want to be back up and running within 24 hours or less.
Generally, says Creighan, it is the CISO who says five days, while the CEO says 24 hours or less.
“This is a massive issue in organizations,” says Creighan, who is vice president for the Asia Pacific at Commvault.
“Let’s just say that those executives who rely on the CISO for their technical analysis and ability often don’t really understand the complexity of the IT environments today. They don’t understand the complexity of multi-cloud, the complexity of application on premises, private cloud or at the edge, or those which are producing data everywhere from IoT devices.”
Complex picture
Creighan’s observations are only a small component of a report that paints a complex picture of security practice and resilience in Australasia.
Based on interviews with over 400 organizations across Australia and New Zealand, the report presents some positive findings, even if these are tempered by global comparisons, and the unrelenting reality that no matter how prepared a company may think it is, it can still be attacked and breached.
For example, the average time for organizations to recover from cyberattacks in the region came down to 28 days from 45 days in the last survey.
While this was a big improvement for Australasia, at 28 days, it was still more than the global average of 24 days.
“It’s like getting into a fight in the schoolyard. You get your butt kicked, but then you start taking lessons to protect yourself.”
Of some concern was the finding that the average dwell time before a cyber incident, and specifically a ransomware attack, saw a “bad or threat actor hanging out in an organization’s IT environment for an average of 199 days.”
“So that is almost 200 days before they actually launched the ransomware attack, and that to me is really scary,” says Creighan.
“Not only are they hanging around waiting for the opportunity, but they are going left, they are going right, and they are trying to find as many credentials as they can and as much information before they make that call and hit the ransomware button.”
Testing, testing
Another insight was related to testing. Even though more than 80% of the organizations surveyed said they had an incident response plan in place, only 30% said they tested their incident response plan across all mission-critical workloads.
“By not testing and not having the right frameworks in place, the thing they struggle to do is find the recovery point of operation, the RPO,” says Creighan.
“This is about understanding where the bad guys got in, and in a lot of situations, that could take a couple of weeks to find out because if you are a major enterprise, you have literally thousands of operations and hundreds of petabytes of data, and you have to work with a forensics technology company to find out. And this is another factor which is stretching the recovery timeframes.”
Of the 30% who said they were testing, many were not testing as rigorously as others.
“Are they doing a table top test, or are they really taking that application down and recovering the application from scratch, rebuilding it and rehydrating the data from a backup source and going step by step through the process,” says Creighan.
“The chances are that they are not.”
Learn how to fight
The Commvault research suggests that organizations that have been breached, on balance, improved their awareness of issues and built a stronger resiliency stance as a result.
“It’s like getting into a fight in the schoolyard, when you don’t know how to fight,” says Creighan.
“You get your butt kicked, but then you start taking lessons to protect yourself.”
While hard-won experience prompted a proactive response, which led to greater resilience, regulators also helped improve outcomes by stipulating data storage requirements, even though many organizations were not fully aware of their obligations.
On the other hand, regulations might be driving better data backup and storage, but around a third of Australasian organizations face conflicting regulatory data demands across different geographies.
The report found that 17% of the responding organizations need to comply with at least four major regulatory acts, with 6% subject to at least six.
Faced with all this, organizations lack confidence in their data management.
The report found that more than half of Australasian organizations lacked confidence in having the necessary relationships, metadata, and configurations required to restore business operations when needed.
In facing a cyber incident, one quarter rated their performance as either ‘bad’ or ‘terrible,’ and only 12% rated themselves as ‘excellent.’
Creighan, however, says that while the struggle for resilience is an ongoing one because of the sophistication of threat actors, there is some “light in the tunnel.”
Organizations that tested regularly and rigorously, enjoyed strong communication between CISOs and senior management, and used AI tools to counter AI threats were more likely to achieve the goal of cyber resilience.
“We call this the concept of continuous business,” says Creighan.
“People used to be focused on business continuity, but now it is continuous business, and the key is to make this a priority, put some money into it and be serious about getting back to that minimum viable company as fast as possible.”
Image credit: iStockphoto/shironosov



Lachlan Colquhoun
Lachlan Colquhoun is the Australia and New Zealand correspondent for CDOTrends and the NextGenConnectivity editor. He remains fascinated with how businesses reinvent themselves through digital technology to solve existing issues and change their business models.